Erebrix Product / AppSec EASM

Continuously validate application and API security.

Erebrix AppSec EASM is an application security management and validation platform that connects attack-surface discovery, API inventory, authorization testing, evidence, findings, remediation, and retesting in one organization-scoped workflow.

Product interface
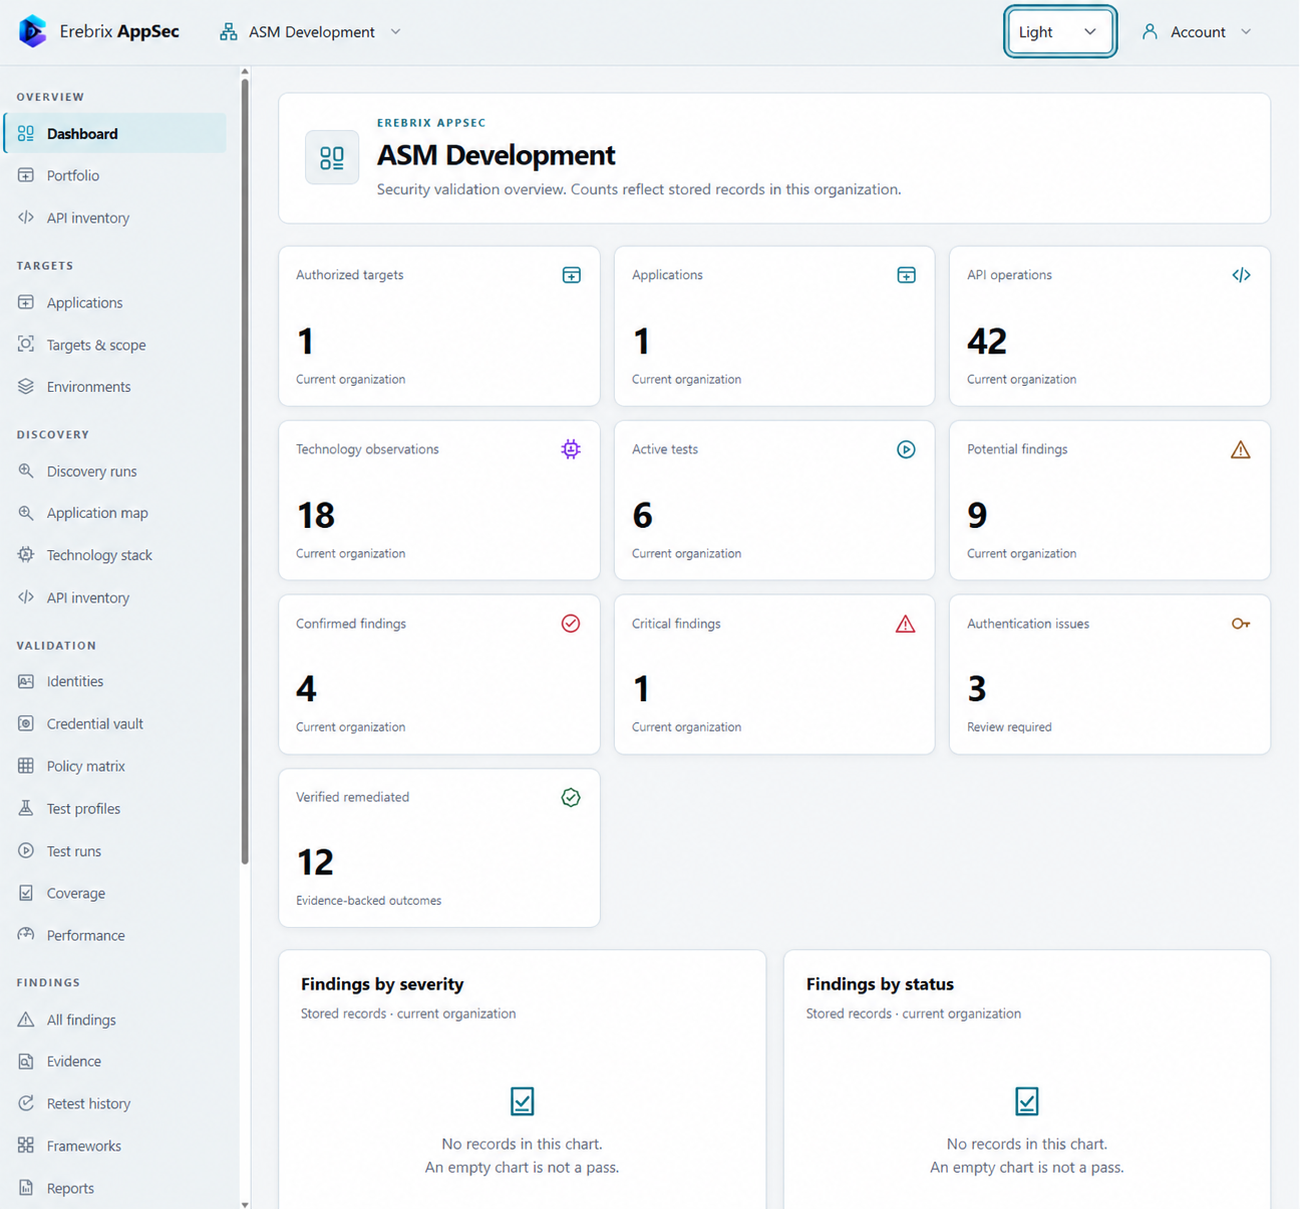
Erebrix AppSec EASM dashboard showing applications, API operations, testing, findings, and remediation metrics.
Application and API security validation overview
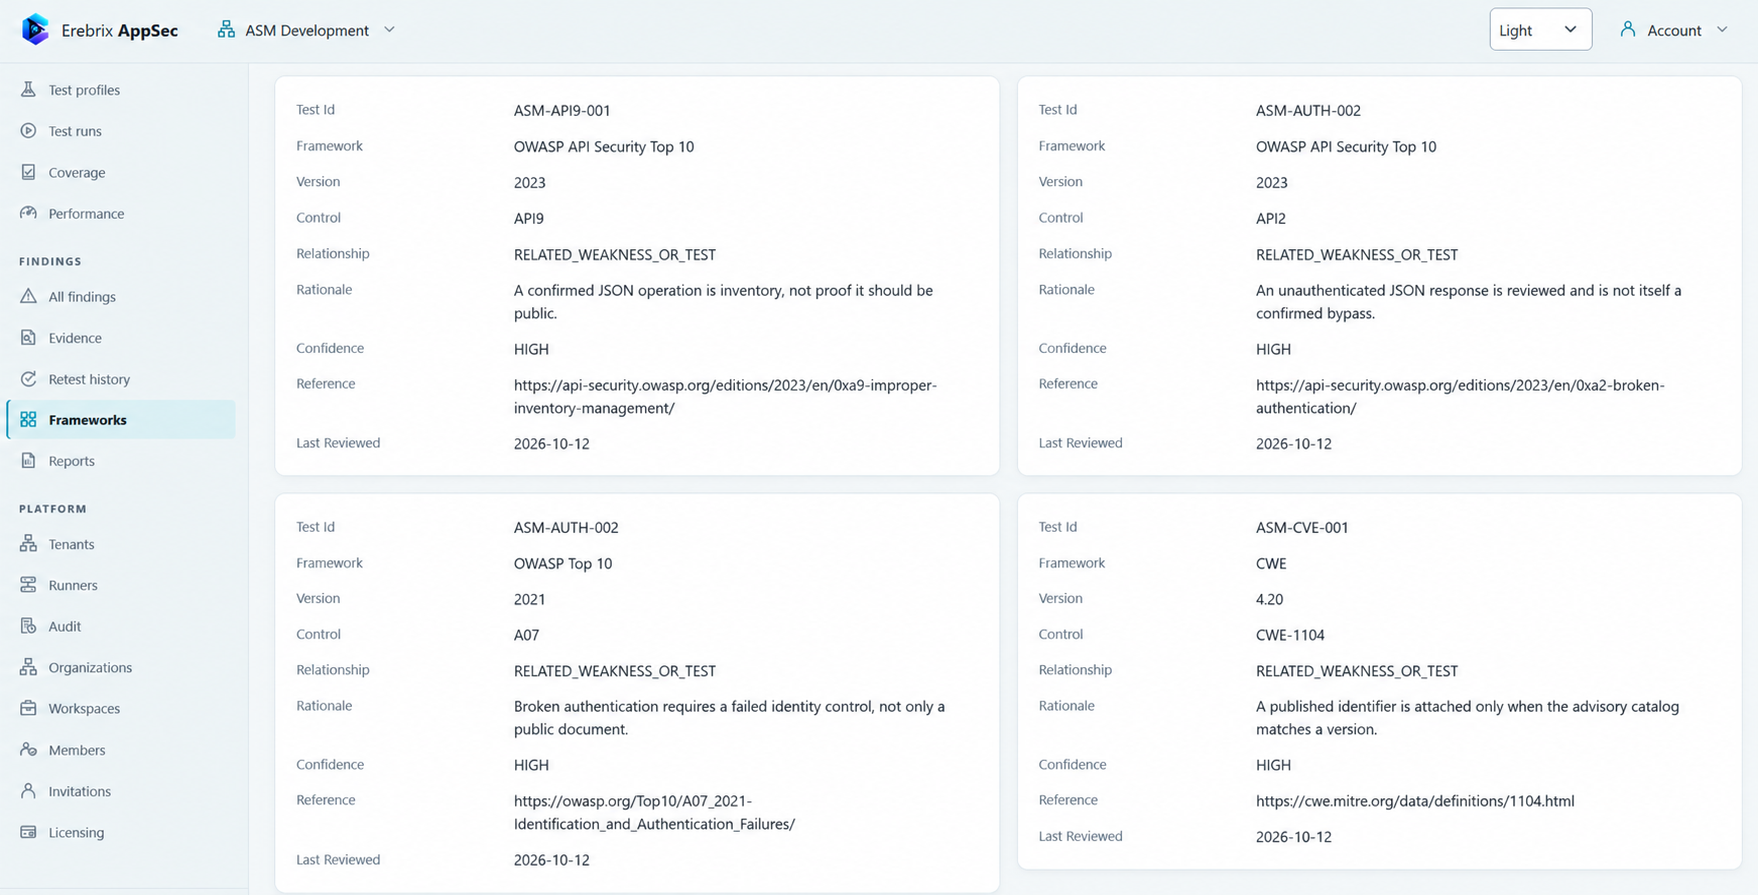
Erebrix AppSec framework mappings showing OWASP API Security, OWASP Top 10, and CWE test rationale and references.
Security framework mappings and validation rationale
Application security visibility

See targets, applications, APIs, identities, and findings in context.

Application and API risk is difficult to manage when discovery, authorization context, evidence, and remediation live in disconnected processes. Erebrix AppSec EASM organizes those relationships around the application environments and targets an organization has authorized for validation.

Continuous validation

Move from discovery to evidence-backed retesting.

The platform combines bounded discovery with policy-driven validation so teams can review what was observed, understand the configured security expectation, preserve evidence, track remediation, and retest the same approved context.

AppSec workflow

Connect the application security lifecycle.

  • Organization, workspace, application, environment, and target hierarchy
  • Authorized target and scope management
  • Bounded HTTP and browser discovery
  • Application mapping and technology observations
  • API inventory and OpenAPI import
  • Encrypted credential and identity contexts
  • Policy-driven authorization validation
  • BOLA and BFLA evaluation for configured policies
  • Sanitized, hashed evidence
  • Finding lifecycle and remediation tracking
  • Version-preserving security retesting
  • Organization-scoped reporting and exports
Controlled testing

Keep security validation tied to explicit authorization.

Targets, scope, identities, policies, assertions, and safety limits are configured deliberately. When the required context is incomplete or observations are inconsistent, the workflow records that the control could not be validated rather than treating uncertainty as a pass.

Product direction

Built for continuous application and API security management.

Erebrix AppSec is actively developed around repeatable security validation, evidence quality, remediation follow-through, and clear organizational context.

Bring application risk into focus.

Explore Erebrix AppSec EASM in the context of your authorized applications and APIs.